Stop Exposing Unreal Engine 5.8 MCP Beyond Loopback Without a Repo Gate - 2026
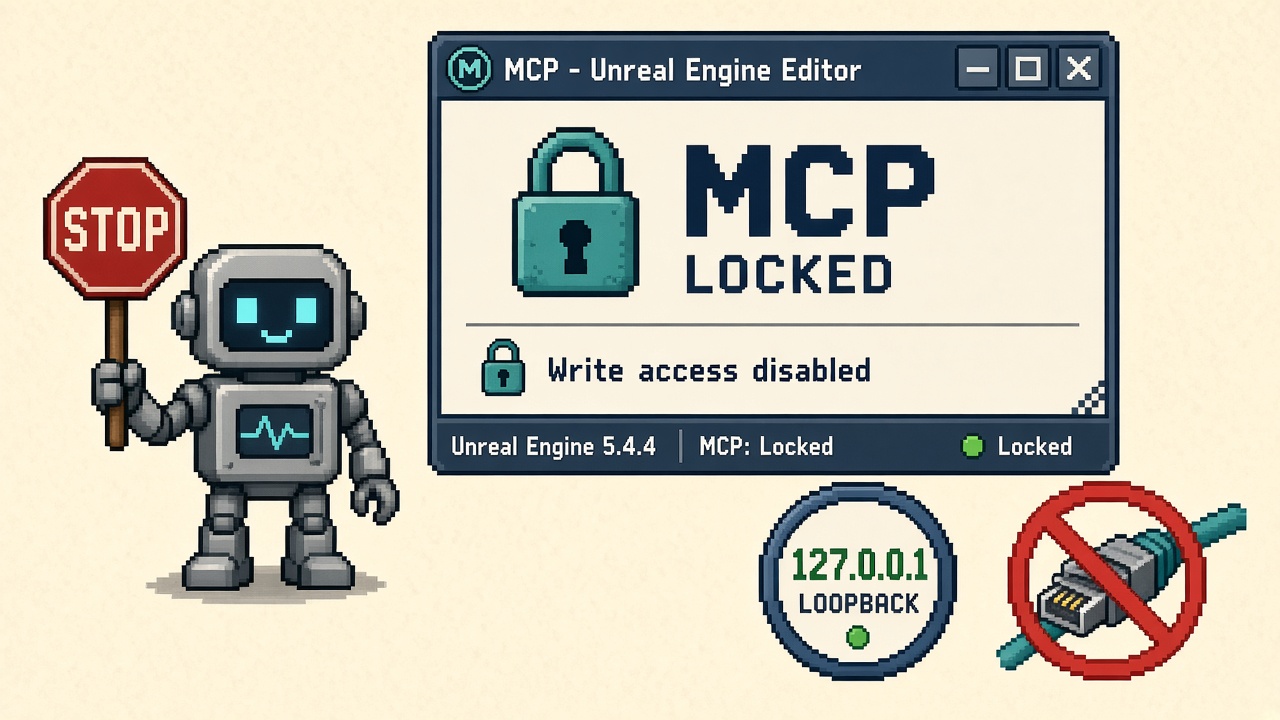
If you searched unreal mcp localhost security after Unreal Engine 5.8 shipped Experimental Unreal MCP, you do not need another “connect Cursor in five minutes” montage. You need a refusal.
Stop exposing Unreal Engine 5.8 MCP beyond loopback without a repo gate. Epic’s own docs say the plugin binds for local use, has no authentication layer, and is not safe to expose beyond the local machine. Port-forwarding 8000, binding “so the remote artist can help,” tunneling through a random ngrok URL, or “just for the Discord playtest” turns an Experimental editor bridge into an unauthenticated remote control surface for your Unreal project. That is not collaboration. That is an incident with a prettier chat UI.
This is not the Claude Code first safe editor session. That URL owns plugins, allowlist tiers, undo, and a first-session receipt. This is not the queued Cursor safe-session worksheet or the free MCP safety tools listicle (sibling backlog rows). This is not Unity MCP with Cursor or Godot AI MCP. Same protocol idea, different engine, different failure: Unreal’s Experimental MCP is explicitly loopback-oriented and unauthenticated. This URL owns the Stop-doing-X position: refuse LAN / VPN / public exposure unless a written repo gate exists — and most indie repos should choose SIT OUT of remote expose entirely.
Lighting cousins (Lumen Lite tools, MegaLights without Lumen Lite Stop) refuse mid-spec GI folklore. This refusal refuses network folklore for an editor agent bridge.
Why this matters now
Unreal Engine 5.8 is now available (June 17, 2026) made official MCP part of the engine conversation. Epic’s Unreal MCP in Unreal Editor documentation is clear in Limitations and Known Issues: the HTTP listener is loopback only by default, the server rejects non-loopback Origin headers, and there is no authentication layer — the plugin is not safe to expose beyond the local machine. Default bind shape in Editor Preferences is http://127.0.0.1:8000/mcp when Auto Start Server is enabled.
Setup SERPs already teach “generate client config and go.” What they under-teach for micro-studios is the sentence after connect: do not treat Experimental MCP as a multiplayer editor API. Agents can spawn actors, touch materials, inspect widgets, and run tools on the game thread. An unauthenticated listener on a reachable interface is not “sharing productivity.” It is sharing write access to whatever toolsets you enabled.
Direct answer: Keep MCP on 127.0.0.1. Run the honesty ladder. If someone asks for remote expose, require a written repo gate (security owner, threat model, auth plan, expiry) — and default to SIT OUT until that gate exists. Pair local sessions with the Claude safe session; do not invent a remote path from this opinion.
Who this refusal is for
| Audience | Use it to… |
|---|---|
| Beginners | Know loopback ≠ “open to the office Wi‑Fi” |
| Developers | Audit bind address, Origin rejection, and “no auth” before any tunnel |
| Creators | Paste a SIT OUT script when someone posts a public MCP URL |
| Companies | CapEx / diligence language for Experimental MCP network risk |
Time: 25 minutes for the ladder; 10 minutes for the sit-out paste.
Honest limit: Epic docs are the authority for bind behavior and the no-auth warning. This opinion argues whether you should expose beyond localhost when the product is Experimental and unauthenticated — almost always no.
Non-repetition
| URL | Job |
|---|---|
| UE 5.8 MCP Claude safe session | First local session — plugins, allowlist, undo, receipt |
| Unity MCP Cursor bridge | Unity bridge + Integrations path |
| Godot AI MCP Cursor session | Godot plugin MCP evening |
| UE 5.8 ship-date lock | Keep/hold on 5.8 features for Gold |
| Lumen Lite tools listicle | GI toolkit — not MCP network policy |
| MegaLights without Lumen Lite Stop | Mid-spec lighting refusal |
| This URL | Stop exposing Experimental Unreal MCP beyond loopback without a repo gate |
Pair packaging side issues later with plugin module packaging help and discovery with 25 free UE 5.5 plugins resources — different problems from unauthenticated remote MCP.
The claim I am refusing
Claim (false): “Unreal MCP is just HTTP — we can bind it on the LAN / VPN / a tunnel so remote teammates (or a cloud agent box) can drive the same Editor, same as sharing a Discord screen.”
Counter-claim: Official Unreal MCP is an Experimental, loopback-oriented server with no authentication. Epic documents that it is not safe to expose beyond the local machine. Remote expose without a written security design is wallpaper collaboration — it looks like teamwork and behaves like an open admin API for whatever Tools you loaded via AllToolsets / Editor Toolset.
Same disease as other Stops: genre wallpaper, demo wallpaper, calendar wallpaper. This is network wallpaper — inventing a multiplayer editor product Epic did not ship.
What Epic actually documents (read before you argue)
From Unreal MCP in Unreal Editor and the 5.8 availability post:
| Fact | Meaning for indies |
|---|---|
| Experimental feature | Incomplete APIs; use caution; expect change |
| Server inside Editor process | Tools run with editor privileges on the game thread |
Default bind 127.0.0.1:8000/mcp |
Local machine only by design |
| Loopback only by default | Non-loopback Origin headers rejected |
| No authentication layer | Anyone who can reach the listener can speak MCP |
| Not safe beyond local machine | Epic’s words — not blog folklore |
| AllToolsets / toolsets enable power | More tools = larger blast radius if exposed |
GenerateClientConfig → .mcp.json |
Points agents at the local URL |
If your appeal strategy is “but HTTP is easy to reverse-proxy,” you are already arguing past the product’s threat model.
Excuse ladder
| Excuse | Why it fails | What to do instead |
|---|---|---|
| “It’s only the office LAN.” | No auth — LAN is still a reachability domain. | Stay on 127.0.0.1; share screen or pair locally. |
| “VPN makes it fine.” | VPN ≠ authentication on the MCP server. | SIT OUT of remote MCP; use VCS + local agents. |
| “ngrok / Cloudflare tunnel is temporary.” | Temporary public URL + no auth = temporary disaster. | Delete the tunnel; kill Auto Start if needed. |
| “We’ll add a password later.” | Product has no auth layer today. | Do not expose until a real design exists (usually never for Experimental). |
| “Firewall will protect us.” | Misconfig and laptop hotspots still happen. | Loopback is the control that matches Epic’s model. |
| “Remote artist needs MCP, not just Parsec.” | Screen share ≠ unauthenticated tool calls. | Pair on one machine; or local clone + local MCP. |
| “Cooked builds can host MCP too.” | Runtime host still needs a security design — not a beginner remote open. | Treat shipping-game MCP as a separate CapEx project. |
| “Unity/Godot people share bridges.” | Different products; Unreal docs are explicit on no auth. | Follow Unreal docs, not cousin folklore. |
| “Port 8000 is obscure.” | Obscurity is not auth. | Loopback + SIT OUT of advertise. |
Honesty ladder (eight rungs)
Answer yes/no without marketing spin. Any hard “no” on rungs 1–5 → SIT OUT of remote expose.
- Is the MCP listener bound to 127.0.0.1 (or documented localhost-only behavior) with no port-forward / tunnel?
- Can you quote Epic: no authentication and not safe beyond the local machine?
- Is every teammate who needs agents running MCP on their own machine against their own Editor?
- Do you refuse public URLs, Discord pastes of
http://…:8000/mcp, and “open for the jam” posts? - If someone proposes remote expose, is there a written repo gate (owner, threat model, auth/network plan, expiry, rollback) — not Slack vibes?
- Are AllToolsets / write-capable toolsets treated as high blast radius even on localhost?
- Is Experimental MCP disabled or Auto Start off on shared CI / build farm machines unless intentionally gated?
- Is a named security/release owner allowed to kill remote-expose folklore the same day it appears?
Print the ladder. Circle the fails. Do not negotiate with yourself on rung 2.
Pattern gallery (not invented studio metrics)
| Pattern | Usually… |
|---|---|
| Local Cursor/Claude → 127.0.0.1:8000/mcp; clean VCS | Pass — then use safe-session URL |
| “Share MCP with the remote contractor over Tailscale” | Fail — no auth |
| Public tunnel “just for tonight” | Fail — kill immediately |
| Bind 0.0.0.0 “so phones can connect” | Fail — refuse |
| Deck slide: “MCP multiplayer editor” | Fail diligence — CapEx refusal |
| Honest SIT OUT + local-only policy in README | Pass as refusal — correct behavior |
| Separate security RFC for future remote tooling | Pass research — not a green light to open Experimental today |
Beginner path — 25 minutes before someone tunnels port 8000
- Open Unreal MCP docs → Limitations and Known Issues. Write: loopback only, no auth, not safe beyond local machine.
- In Editor Preferences → Model Context Protocol, confirm bind is localhost /
127.0.0.1and note port (often 8000). - Check your OS for port forwards, WSL republish, Docker
-p 8000:8000, and active tunnels. Kill any that map MCP outward. - Run the eight-rung ladder aloud with a teammate.
- Decision: PAIR-LOCAL / SIT-OUT-REMOTE / REPO-GATE-REQUIRED (almost never green same day).
- Paste the sit-out script if remote folklore already started.
- If you still need a first local session, open the Claude safe session — not a tunnel guide.
Common beginner mistakes:
- Pasting the MCP URL into Discord “so others can try.”
- Assuming VPN membership equals authenticated MCP.
- Confusing screen-share collaboration with tool-call collaboration.
- Enabling AllToolsets on a machine that also has casual port forwards.
Developer path — gates L1–L6
| Gate | Check | Pass if… |
|---|---|---|
| L1 | Bind literacy | Documented listener is loopback-only; no 0.0.0.0 intent |
| L2 | No-auth literacy | Team can quote Epic’s no-auth / not-safe-beyond-local lines |
| L3 | Reachability audit | No tunnel, no NAT forward, no cloud publish of :8000/mcp |
| L4 | Tool blast radius | Write toolsets only on localhost sessions with allowlist (safe session) |
| L5 | Diligence line | CapEx four-liner signed |
| L6 | Decision latched | PAIR-LOCAL / SIT-OUT-REMOTE / REPO-GATE-REQUIRED in receipt |
Fail closed: L1–L3 fail → SIT-OUT-REMOTE even if “it would be convenient for the remote lighting pass.”
Repo gate (what “written gate” means — and when to refuse anyway)
A repo gate is not a Discord thumbs-up. Minimum fields before anyone even discusses non-loopback:
| Field | Required content |
|---|---|
| Owner | Named security or tech lead |
| Threat model | Who can reach the listener; what Tools can do |
| Auth plan | How identity works — Experimental MCP has none today |
| Network plan | Bind, TLS, allowlists, expiry |
| Rollback | How to kill the listener in <5 minutes |
| Scope | Which project, which machines, which dates |
| Sign-off | Written APPROVED / REJECTED |
Default for Experimental Unreal MCP: REJECT remote expose. The gate exists so “maybe later” cannot silently become “we opened ngrok at 2am.” If auth does not exist in-product, the honest gate outcome is SIT OUT, not “open and hope.”
Exception myths (extra refusals)
| Myth | Reality |
|---|---|
| “Rejecting non-loopback Origin is enough auth.” | Origin checks are not authentication. |
| “Only our CI can hit it.” | CI networks are still multi-tenant risk surfaces. |
| “Read-only tools make remote OK.” | Tool surface changes; Experimental; still no auth. |
| “We’ll use a random high port.” | Obscurity ≠ security. |
| “Contractors signed an NDA.” | NDA ≠ network auth on MCP. |
Sit-out script (Discord / Slack paste)
Stop: we are not exposing Unreal Engine 5.8 Experimental MCP beyond loopback.
Reason: Epic documents loopback-only defaults, no authentication layer, and
"not safe to expose beyond the local machine."
Decision: SIT-OUT-REMOTE — local 127.0.0.1 sessions only.
No tunnels, no LAN bind, no public MCP URLs, no "temporary" ngrok.
Repo gate required before any future remote design — default REJECT while Experimental + no auth.
Safe local path: first-session allowlist on the same machine as the Editor.
Owner: ____
Receipt: docs/unreal_mcp_loopback_refusal_receipt_v1.json
Creators: paste this when someone already scheduled a “shared MCP jam.” Then revoke any published URL the same hour.
PAIR path (local only — what green looks like)
If you pass L1–L3 and only need local agent productivity:
- Keep Auto Start / StartServer on 127.0.0.1.
- Generate client config with
ModelContextProtocol.GenerateClientConfigfor Cursor/Claude — do not hand-type remote hosts. - Follow allowlist + read-only smoke on the Claude safe session.
- Treat AllToolsets as a privilege escalation on localhost too.
- Latch PAIR-LOCAL in the receipt below.
Remote teammates get: Git branches, reviewed PRs, screen share, or their own local Editor + MCP — not your open listener.
Before / after claim patterns
Wallpaper (fail): “Here’s our studio MCP endpoint — connect from home and drive the main map.”
Honest local (pass shape): “MCP stays on 127.0.0.1 on each artist’s machine. No shared remote Unreal MCP while Experimental and unauthenticated.”
Honest sit-out: “We refuse remote MCP expose. Local agents only. Repo gate default REJECT.”
Honest research (not a green light): “Future remote tooling needs auth + threat model — not tonight’s ngrok.”
The fix is not adding the word “secure” to the README. The fix is not opening the port.
Worked decisions (fill your project name)
Studio A — remote lighting contractor asks for MCP URL
- Contractor has VPN.
- Wants to run Cursor against the lead’s Editor overnight.
Decision: SIT-OUT-REMOTE. Offer screen share or a branch on the contractor’s machine with local MCP. VPN ≠ auth.
Studio B — jam posts public tunnel “for friends to try AI level gen”
- Discord event energy.
- AllToolsets enabled.
Decision: Kill tunnel immediately. SIT-OUT-REMOTE. File incident note. Re-read Epic limitations aloud.
Studio C — producer deck claims “MCP multiplayer Unreal editing”
- Fundraising narrative.
- No security owner.
Decision: CapEx refusal + scrub deck. PAIR-LOCAL only in product language.
Studio D — clean local Claude session, no remote ask
- 127.0.0.1; allowlist; receipt filed on safe-session URL.
Decision: PAIR-LOCAL. This Stop does not block you — you already passed.
Studio E — build farm experiments with -ModelContextProtocolStartServer
- Curious about cooked-build MCP hosts.
Decision: Separate CapEx project. Do not conflate with editor loopback sessions. Default deny on reachable interfaces until a real auth design exists.
Incident and reputation risk (why network wallpaper is expensive)
| Wallpaper move | Near-term “win” | Likely cost |
|---|---|---|
| Public MCP URL in Discord | Jam hype | Unauthenticated tool calls; map corruption; secrets adjacent |
| LAN bind for “office AI” | Convenience | Lateral movement from any compromised laptop |
| VPN-only expose without auth | False comfort | Any VPN principal = MCP principal |
| Tunnel “just tonight” | Demo theater | Screenshots of your endpoint live forever |
| Silence after a weird tool call | Avoid awkwardness | No rollback owner; repeated incidents |
Experimental MCP teaches studios whether they treat agent bridges as local power tools or internet services. Teaching the team that “HTTP means shareable” is harder to undo than missing one Cursor evening.
Thirty-minute team agenda (copy)
- 0–5 min — Read Epic Limitations (loopback, no auth, not safe beyond local) aloud.
- 5–12 min — Audit machines for tunnels / forwards / published URLs.
- 12–20 min — Score L1–L6; screenshot bind preferences.
- 20–25 min — Choose PAIR-LOCAL / SIT-OUT-REMOTE / REPO-GATE-REQUIRED.
- 25–30 min — Latch receipt; assign scrub owner for any public posts.
No “temporary tunnel” tickets leave this meeting alive.
CapEx four-liner
- Asset at risk: Project integrity + IP + contractor trust + Experimental feature reputation.
- Change proposed: Expose Unreal 5.8 MCP beyond loopback (LAN/VPN/tunnel) without product auth.
- Cost if wrong: Unauthorized editor tool calls, content loss, diligence failure, incident write-up.
- Decision owner: Tech lead / security owner; default = SIT-OUT-REMOTE.
PAIR / SIT OUT / RECOVERY scripts
PAIR-LOCAL:
“MCP on 127.0.0.1 only. Safe-session allowlist. No remote listeners. Receipt filed.”
SIT-OUT-REMOTE:
“We refuse exposing Experimental Unreal MCP beyond loopback. No auth → no remote. Local agents only.”
RECOVERY (already published a URL):
“Correction: we are shutting down the shared Unreal MCP endpoint. Epic’s Experimental MCP has no authentication and is not safe beyond the local machine. Use local Editor + local MCP only. Thanks for the report — incident owner is ____.”
Receipt — unreal_mcp_loopback_refusal_receipt_v1.json
Use for PAIR-LOCAL or SIT-OUT-REMOTE — decision carries the truth.
{
  "receipt_type": "unreal_mcp_loopback_refusal_receipt_v1",
  "project": "REPLACE",
  "engine": "UE_5.8",
  "filled_at": "2026-10-12",
  "decision": "SIT_OUT_REMOTE",
  "bind_host": "127.0.0.1",
  "bind_port": 8000,
  "tunnel_or_forward_found": false,
  "ladder_fails": [],
  "gates": {
    "L1_bind_literacy": false,
    "L2_no_auth_literacy": false,
    "L3_reachability_audit": false,
    "L4_tool_blast_radius": false,
    "L5_capex": false,
    "L6_latched": false
  },
  "repo_gate_status": "REJECT_DEFAULT",
  "public_url_scrubbed": false,
  "owner": "",
  "notes": ""
}
Key takeaways
- UE 5.8 Unreal MCP is Experimental — cite Epic news + docs.
- Loopback only by default —
127.0.0.1is the product model. - No authentication layer — Epic says not safe beyond the local machine.
- This URL owns the refusal — safe-session URL owns local first evening.
- L3 reachability audit ends tunnel arguments.
- VPN ≠ auth.
- Repo gate default REJECT while Experimental + no auth.
- PAIR-LOCAL is allowed — remote expose is not.
- AllToolsets raises blast radius even on localhost.
- CapEx four-liner makes the risk speakable.
- Receipt JSON beats “we thought LAN was fine.”
- Primary keyword: unreal mcp localhost security.
FAQ
Is Unreal Engine 5.8 MCP safe to expose on the internet?
No. Epic documents no authentication and states the plugin is not safe to expose beyond the local machine. See Unreal MCP docs.
Does loopback-only mean office LAN is OK?
No. Loopback means the local machine (127.0.0.1 / localhost), not “anyone on the same Wi‑Fi.”
Is a VPN enough to share Unreal MCP with remote teammates?
No. VPN membership is not an authentication layer on the MCP server. Prefer local Editors per person or screen share — not a shared unauthenticated listener.
How is this different from the Claude Code safe session post?
That safe session teaches a local first evening (plugins, allowlist, undo). This page is the Stop opinion that refuses remote / LAN / tunnel expose without a written repo gate.
Can cooked games host MCP servers?
Epic notes runtime modules can host a server, but that is a separate security project — not permission to open Experimental editor MCP on a public interface.
What should we do if we already posted a public MCP URL?
Kill the tunnel/forward, stop the server (ModelContextProtocol.StopServer), scrub posts, file the recovery script, and latch SIT-OUT-REMOTE in the receipt.
Do Unity or Godot MCP posts change this Unreal rule?
No. Cousin engines have their own bridges. Unreal’s documented no auth / not safe beyond local line is decisive here.
What primary keyword does this page target?
unreal mcp localhost security — Stop opinion for exposing Experimental Unreal MCP beyond loopback.
Related reading
- Unreal Engine 5.8 MCP with Claude Code - First Safe Editor Session 2026 — local first-session sibling
- Unreal 5.8 MCP - First Indie Safe Cursor Session Worksheet 2026 — Cursor fill-in worksheet (local only; not remote expose)
- 12 Free Unreal MCP Agent Safety Tools After UE 5.8 - 2026 — free safety toolkit (local instruments; not a remote green light)
- Unity MCP with Cursor - First Safe Editor Bridge Session 2026 — Unity cousin
- How to Use Godot AI MCP with Cursor - First Safe Editor Session 2026 — Godot cousin
- Unreal Engine 5.8 What Micro-Studios Should Lock Before Betting a Ship Date - 2026
- 12 Free Unreal Lumen Lite Tools After UE 5.8 - 2026 — same engine wave, different job
- Stop Shipping Unreal MegaLights Mid PC Demos Without Lumen Lite - 2026
- Claude Code Manual Permission Mode - Game Developers What Changed 2026
- Unreal Packaging Fails - Plugin Not Found Module Fix
- 25 Free Unreal Engine 5.5 Plugins and Marketplace Assets
Primary sources: Unreal MCP in Unreal Editor · Unreal Engine 5.8 is now available.
Conclusion
Experimental Unreal MCP is a local power tool, not a multiplayer editor API. Epic already wrote the hard part: loopback defaults, no auth, not safe beyond the local machine. Stop inventing remote expose folklore. Keep 127.0.0.1. Pair locally. File the receipt. Default the repo gate to REJECT until a real security product exists — which today’s Experimental plugin is not.
File the receipt. Paste Discord. Stop opening port 8000 to the world.